- Joined
- Mar 7, 2023
- Messages
- 83
- Reaction score
- 19
Hello 3CX Team,
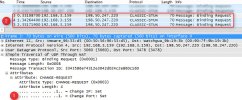
After upgrading our 3CX system to V20 Update 10 (Build 1801), the Firewall Checker repeatedly failed the Full Cone NAT tests for UDP 5060 and multiple RTP ports.
We're using a Palo Alto PA-1420 firewall with restricted inbound and outbound rules based on the STUN server IP addresses published in the official 3CX documentation:
https://www.3cx.com/docs/firewall-checker/
During troubleshooting, we discovered that our Palo Alto was denying incoming UDP traffic from 34.73.139.160 to multiple RTP ports (9042, 9052, 9060, 9066, 9072, and 9076).
This IP address is not included in the official 3CX Firewall Checker whitelist.
After adding this IP to our restricted firewall address group, the previously failing firewall tests started passing.
I also found a German 3CX Community Forum discussion reporting a similar issue involving secondary STUN response addresses (34.159.93.50):
https://www.3cx.de/forum/threads/fi...bes-nachweislich-bei-der-pbx-ankommen.127080/
Could the 3CX team please confirm whether 34.73.139.160 is an official secondary STUN response server and update the Firewall Checker documentation to include it?
Administrators using source-IP-restricted firewall policies rely on this documentation to properly configure their firewalls without allowing unrestricted inbound traffic.
Thank you!
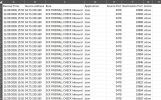
After upgrading our 3CX system to V20 Update 10 (Build 1801), the Firewall Checker repeatedly failed the Full Cone NAT tests for UDP 5060 and multiple RTP ports.
We're using a Palo Alto PA-1420 firewall with restricted inbound and outbound rules based on the STUN server IP addresses published in the official 3CX documentation:
https://www.3cx.com/docs/firewall-checker/
During troubleshooting, we discovered that our Palo Alto was denying incoming UDP traffic from 34.73.139.160 to multiple RTP ports (9042, 9052, 9060, 9066, 9072, and 9076).
This IP address is not included in the official 3CX Firewall Checker whitelist.
After adding this IP to our restricted firewall address group, the previously failing firewall tests started passing.
I also found a German 3CX Community Forum discussion reporting a similar issue involving secondary STUN response addresses (34.159.93.50):
https://www.3cx.de/forum/threads/fi...bes-nachweislich-bei-der-pbx-ankommen.127080/
Could the 3CX team please confirm whether 34.73.139.160 is an official secondary STUN response server and update the Firewall Checker documentation to include it?
Administrators using source-IP-restricted firewall policies rely on this documentation to properly configure their firewalls without allowing unrestricted inbound traffic.
Thank you!