Suspected International Call Fraud

Martin_George

Premier Customer
Joined
Aug 11, 2020
Messages
6
Reaction score
0
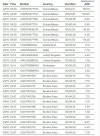
I can see some fraud call in the Telecom provider invoice for October 2026......these calls are not showing in 3CX reports....

Any idea how this could have been happened?

My findings indicate that the suspicious calls were limited to three days (22, 24 and 25 October), involving 65 calls to Guinea-Bissau and Burkina Faso, with total charges of approximately AED 2,818.
 

Attachments

  • Fraud Calls.jpg
    Fraud Calls.jpg
    111.2 KB · Views: 11
if theyre not in 3CX reports then they didnt originate from 3CX.
 
@Mujahed Khan check if the trunk is registered anywhere else, like another PBX.
From the portal of your Telecom provider can you see the source ip of the trunk registrations ?
 
Thanks for your response.

Just to clarify, we're using a physical PRI line, connected to our 3CX system through a Patton gateway.

The suspicious international calls appear on our invoice but are completely absent from our 3CX call logs.

In this setup, can we conclusively rule out 3CX if the calls are not reflected in its reports? Or is there any possibility of calls being initiated through the PRI gateway or another route without being recorded in 3CX?

I'm trying to establish whether we should focus our investigation entirely on the telecom provider and PRI gateway, or whether there are any additional checks we should perform within 3CX.

Appreciate your guidance.
 
@Mujahed Khan if the calls do not appear on the Reports of the PBX, then the calls were not made from the PBX side.
Yes you can rule out this scenario.
Check the Patton gateway in case there are anyregistrations from any other internal ip.
 
Just to be certain, your call logs still remain? They werent purged? You can see calls in your report?
 
@Alphabetic - Yes, all over call logs are there in 3CX except thee fraud calls happend on October 23, 24 and 25......These fraud calls are only showing in Telecom provider invoice. We have a simple setup - 3CX on-prem server, Patton gateway and a PRI line.....Im wondering this would have happened....
 
@NikosT_3CX - its a valid point....let me check the Patton gateway......Is the call fraud at PRI Line Patton gateway level common? If the gateway has accepted calls from another internal IP, would those calls bypass 3CX entirely and therefore not appear in the 3CX call reports? Just curious?
 
@Mujahed Khan
.Is the call fraud at PRI Line Patton gateway level common?
>> Not really but you never know in these cases.. Since this is local the requests may come from another internal ip.

If the gateway has accepted calls from another internal IP, would those calls bypass 3CX entirely and therefore not appear in the 3CX call reports?
>> Exactly, these would never appear on the PBX side if the calls did not initiate from an endpoint that belongs to the PBX.

Think that someone has the credentials of the gateway and goes and registers a client on it and starts making calls firectly towards the gateway. The PBX would never know that.

But again, this is just a idea to check it out.
 
The most likely cause is a virus enabled someone somewhere on your network to install SIP software and register to your Patton. This is not likely a problem with 3CX unless they were able to get the Patton password by looking at your 3CX configuration.

First, talk to your SIP providers. They can implement safeguards like blocking countries, set up spending limits, etc. That's the fastest way to stop the bleeding.

Second, I would do a complete deep virus scan on every PC, laptop, server, Pi, phone, or any other device connected to your network. If a device has had, or has, access to your network either locally or over VPN, or through software like TailScale, you better check everything everywhere including home PCs (don't forget your kids' devices). There is limited benefit to changing passwords until you have removed keyloggers and the like off of all your devices.

Third, start changing your password everywhere. I would start with your Patton, especially if it is still using the default password. !Password01! is not a complex password.

If it was indeed just 3 telephone calls, dude, consider yourself very, very lucky. Over the last 20+ years I've seen customers where hackers ran up thousands of dollars in international phone calls in a matter of an hour or less. About 15 years ago, one of our customers initiated this exact process by responding "Yes" to an error that said they had a virus and they needed to install the latest anti-virus patches. Keep your eyes focused on this and tell people to think before they say "yes".
 
Similar incident happened with our client in UAE, same setup. same fraud calls, excessive billing, E1 provider disconnected the line for over billing .

i suspect Patton gateway are accepting request from any ip may have caused this.
 
Most porbably this is the case as since calls are not shown in the PBX then are they are not orginated from the PBX but from Gateway.
This has to be reported to vendor for further investigation with their logs.
 

Latest Posts

Forum statistics

Threads
112,542
Messages
593,112
Members
165,751
Latest member
Teresa Nguyen