


- Joined
- Mar 25, 2020
- Messages
- 2,674
- Reaction score
- 1,587
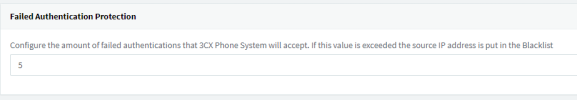
At the moment there are just the sip attempts configurable. Would it not make more (security) sense to 'publish' BOTH thresholds in the GUI and let the (paranoid) admins decide, in stead of a hard-code, arbitrary value?
And while we are at it, in another thread someone also suggested 'protecting' the console login with an extra 2FA possibility?
And while we are at it, in another thread someone also suggested 'protecting' the console login with an extra 2FA possibility?

Upvote
98


