Solved Wrong servername in client hello when using tls

Status
Not open for further replies.

mkoster

New User
Joined
Dec 8, 2021
Messages
3
Reaction score
0
I am testing out 3cx with my voip provider. When I register without tls everything works. But when I try to register over tls is going wrong.

When I look at the wireshark trace I see that the client hello has the 'wrong' servername.
Instead of the outbound proxy name the Registrar/Server/Gateway Hostname or IP is used in de client hello.
This is not the name on the certificate so the tls connection is reset.

Is there an option to set the servername that is used in the client hello for the tls negotiation ?


To test I set the registrat to the name of the outbound proxy and the tls negotiation goes ok, but the registration fails because the outbound proxy is not the sipdomain

I am using the Generic Sip trunk profile with 3CX version 18
 
Hi @mkoster

The SIP domain used is always the value in the Registrar/Server/Gateway Hostname or IP either its TLS on not so the provider needs to advertise that in the server hello and the certificate negotiation.
There is no option in 3CX to use the outbound proxy as the SIP domain.
 
thats strange because you connection to the address of the outbound proxy so that should be used as servername in de client hello not the sipdomain.

sipdomain of my provider is not resolvable
 
Yes, you are correct. When a proxy is available the PBX will resolve and connect to that. The reason why you have a separate proxy and a different SIP domain though is because its the SIP domain that needs to be used in the SIP headers. Otherwise your provider would only give you a proxy address and call it a day.
You said so your self that if you use the proxy as SIP Domain the registration fails. And your provider might might have multiple proxies for load balancing or different regions or failover but the SIP domain is always the same and that should be used for TLS. That way you need 1 certificate for all proxies.
 
The registration fails because the outbound proxy name is not the sipdomain that true.

But to negotiatie tls/ssl the client hello should contain the outbound proxy name not the sipdomain, because you connect to the outbound proxy not the sipdomain. And with our provider the sip domains are not resolvable.

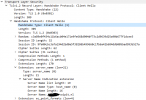
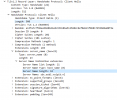
I attached two screenshots from a client hello. One is from a Yealink phone on tls. The other is from the 3cx.
The screenshot from the Yealink show the address of the outbound proxy as should and registers without a problem. When I use the same settings in 3cx it doesn't work because of the wrong servername in de client hello
 

Attachments

  • 3cx_client_hello.PNG
    3cx_client_hello.PNG
    23.2 KB · Views: 8
  • yealink_client_hello.PNG
    yealink_client_hello.PNG
    24.8 KB · Views: 7
Based on what I read in the RFC3261 the certificate should be issued to the address that will also be used in the registrar address.
Code:
   The registrar SHOULD offer a certificate to the UA, and the site
   identified by the certificate MUST correspond with the domain in
   which the UA intends to register; for example, if the UA intends to
   register the address-of-record '[email protected]', the site
   certificate must identify a host within the atlanta.com domain (such
   as sip.atlanta.com)

Code:
   The UA then creates a REGISTER request that SHOULD be addressed to a
   Request-URI corresponding to the site certificate received from the
   registrar.

From the above i gather that everything should be matching. So if you use the registrar address or the SIP domain then the certificate should be addressed to the same domain.

Regardless of what is the best practice, that is how 3CX is handling this and that is not going to change anytime soon. So you can either choose a 3CX supported provider which does TLS or keep using your provider without TLS.
 
Status
Not open for further replies.

Latest Posts

Forum statistics

Threads
112,324
Messages
591,897
Members
165,476
Latest member
awan05