- Joined
- Mar 2, 2026
- Messages
- 2
- Reaction score
- 0
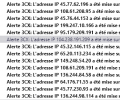
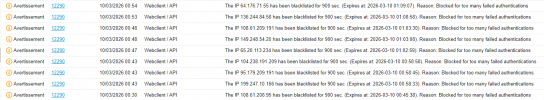
The system is getting constantly targeted and attacked by random public IP addresses that are attempting to authenticate in. This is occurring consistently roughly every 5 minutes.
Its getting to a point that it is affecting call quality and latency. We have made it so the console is only accessible from a specific IP address but that doesn't seem to have stopped the attacks.
Is there anything I can change on my end to prevent these attacks from occurring?
Thanks for your support!