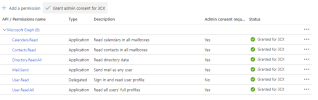
Azure AD integration MS Graph permission

Status
Not open for further replies.

CodeTwo

Customer
Joined
Jun 27, 2017
Messages
42
Reaction score
3
Based on article: https://www.3cx.com/docs/manual/microsoft-365/ Azure AD integration require Directory.Read.All permission which allow 3CX app to read all directory properties. This is potential security issue as directory might contain sensitive information. Can I use User.ReadBasic.All instead? This permission allow access to following attributes:

  • displayName
  • givenName
  • mail
  • photo
  • surname
  • userPrincipalName
 
I would use the correct permission. Security isn't a problem as long as it's readonly. Also, those fields aren't enough for the integration.
 
Do you know what attributes are required to integrate with Azure AD? I know in most cases read-only isn’t problem however we have attributes that we don`t want to expose to external applications.
 
  • Like
Reactions: Evolute IT
The Directory.Read.All permission allows the app to read data, such as users, groups, etc., and is essential for the 365 sync process.
 
Status
Not open for further replies.