Direct routing port and user read access

Status
Not open for further replies.

garnesdata

Silver Partner
Advanced Certified
Joined
May 25, 2020
Messages
39
Reaction score
6
Hi guys

I have a few customers sharing a big O365 tenant which is managed by other service company.I thought it might be a problem creating multiple trunks with direct routing using the same port, 5062. I changed the port used by 3cx in the parameters on our own 3cx system and it works, now using 5069. Do you know if the teams tenant can handle multiple trunks with the same port?

Another question. The sys admins for this tenant had a problem with providing the app (azure) full permission on reading the users, Users.read.all. Is it possible to create a read permission only for certain domains?

Björn
 
Hi Björn,

Just to make sure I understand your questions and scenario, you have 1 O365 tenant and multiple 3CX installations, and you want:
- Some users of the O365 Tenant to have User sync and Teams Integration with 3CX server A
- Some others users of the O365 Tenant to have User sync and Teams Integration with 3CX server B
- etc...
?
Correct.
 
Ok, so the answer is "Yes", but you need to bit a bit careful setting everything up.

First off, for each 3CX installation, you want to do a unique App Registration.

Once you have done that, for User Sync make sure you choose the "Only these users" option in the "User Sync" tab and select only the users you want to sync on this 3CX installation.
Do the same for the other 3CX installations as well.
Follow similar logic for SSO, Contact sync and Calendar Sync.

For Teams, it's a bit more tricky. for each 3CX installation you need a unique "Teams FQDN" which also means a unique SSL cert for each one (remember, you can't use wildcard certs...).
Once you have that configure it and download the 2 Powershell scripts but don't run them immediately!
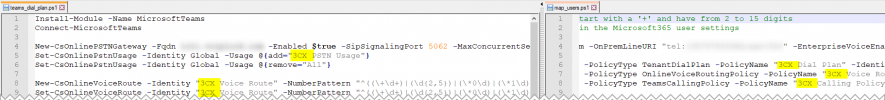
Open each pair of scripts of each site with a next editor and use the "Find and Replace" function to:
  • Find "3CX " (without the quotes, including the space)
  • Replace with "3CX Site A " (without the quotes, including the space)
Your goal is to change all the Identity values in the scripts so that they are unique for each site, and not overlap with each other, while correctly still referencing each other.
1637155787301.png

If you do everything correctly, your will get what you want.


[EDIT]
I forgot to mention, I am not sure why you changed the Port Number, for what you want to do, this isn't necessary unless you have multiple 3CX installations behind the same Public IP Address, which we don't recommend in the first as you would have more ports overlapping as well.
 
  • Like
Reactions: Evolute IT
Ahh I think I wasn't clear on this, sorry. I know how to edit the scripts and use multiple trunks from one tenant, we are managing other tenants with other SBC's for Direct routing. I asked about the port since I wasn't sure the Teams tenant would accept multiple trunks using the same port number - I just changed the port myself to try this out and because I can :)
Regarding the unique App Registration; the sysadmins are not happy about exposing this information to the app - that you can read all the users from the tenant. They want restriction on that, preferably by using specified domain.
 
Regarding the unique App Registration; the sysadmins are not happy about exposing this information to the app - that you can read all the users from the tenant. They want restriction on that, preferably by using specified domain.
You can experiment with the security settings of an individual app Registration of course, but you are going into "uncharted waters".
 
Status
Not open for further replies.