inhouse hosted 3cx and Meraki mx64

Status
Not open for further replies.

sulli86

Silver Partner
Basic Certified
Joined
May 16, 2019
Messages
26
Reaction score
0
Hello,

I know there has been mixed reviews regarding meraki and the MX64, however we seem to be having issues.

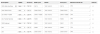
when we run the firewall test we are getting "mapping does not match 5060 mapping is 38957, or different port for each test
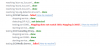
13241

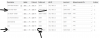
then from port 10600 to 10998 we are getting full cone test failed
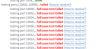
13242

This appears to be causing issues with Stun for phones at remote sites at times, the 3cx is running 16.3, we are also waiting to hear back from Meraki but they are confused as well
 
Not what you want to hear but I have historically had a whole bunch of issues with Meraki and VoIP I really would not recommend using them together.

We use VPN's for connecting our phones and even then there was something odd going on.

Stun for phones

Recommended on 3CX documentation for only 1-2 phones per site and I agree, a lot of configuration is required for these including local router port forwarding, static IP address allocation and provisioning of correct and incremented ports on the phones.
 
Hi @sulli86

You don't mention whether you set up your ports on this device.
https://www.3cx.com/docs/ports/

I believe it offers 1:1 NAT if you enable it, but if it does not honor the settings you may have to consider a different router/firewall solution otherwise you may end up troubleshooting your PBX aimlessly for intermittent problems.
 
Hey @JohnS_3CX

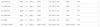
I have port Forwards setup, but cant setup 1 to 1 Nat on the firewall for default WAN address
13246
 
Hi @sulli86

I see. So 1:1 NAT is a must, you can't have port remapping and still expect to have a reliable system. I would say that the device is not compatible in this case. Not saying it wont work at all, but I would expect issues every now and then with audio and registration.

You can run it and see how it goes but it is not a supported scenario if you are using internet based trunks. I guess you can get away with it for gateways (since the traffic is local between PBX and gateway) but you may still face issues with webclients, clients, webmeeting.

I'm guessing this is a local on premise 3CX instance yes?
 
this is not well set no?
13248
 
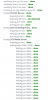
We use the MX64 and 3CX all the time and I have never had any issues:

13249
 
Hi @hogan71088

Thanks for sharing your setup. Does the firewall checker pass with your above setup?
 
Hi @hogan71088

Thanks for sharing your setup. Does the firewall checker pass with your above setup?

Yep it passes. Meraki is actually one of the few firewalls I work with where there's no issues...

13250
 
Hi @hogan71088

Thanks for sharing your setup. Does the firewall checker pass with your above setup?
I have a MX64 too and we never had issues.

However, I recommend anything else simply because Meraki is expensive. It's for certain use-cases only.
 
Hello all,

Thanks for the assistance, I have cleaned up my firewalls rules as @aws2p pointed out and used the same settings as @hogan71088 with no change from the firewall settings side, the issue is the phone is currently operating correctly but firewall failure meaning it may not be reliable
 
Did you reboot MX64 after rule change ?
 
Did you reboot MX64 after rule change ?
Yeah i did, i even rolled back from Beta to stable, the reason we are running Beta is a ubiquiti router and the meraki didn't play nice for VPN until Beta was enabled.

would you get a false positive if stun devices are trying to communicate with the phone system while doing the firewall test?
 
would you get a false positive if stun devices are trying to communicate with the phone system while doing the firewall test?
Sorry , no idea
 
this is what Meraki came back with

  • The phone system fails for ports 10000 and above
  • Took packet capture on bot WAN and LAN interface
  • Sent the packet captures to the Cx
  • The packet capture shows 4 set of Classic STUN request and response
  • For the first set of request the server (54.39.182.217) responds back with attribute source address port 3478
  • For the second set of request the server (54.39.182.217) responds back with attribute source address port 3479
  • The client 192.168.0.3 sends another request with destination port 3478 whereas the response was from the source port 3479. When we checked the packet capture with ump.port==9342 there are only two sets of request and response and it stopped after the second set of request the server (54.39.182.217) responds back with attribute source address port 3479
  • Cx to further analyse the packet capture and call back if required
 
Yeah i did, i even rolled back from Beta to stable, the reason we are running Beta is a ubiquiti router and the meraki didn't play nice for VPN until Beta was enabled.

would you get a false positive if stun devices are trying to communicate with the phone system while doing the firewall test?

Hi @sulli86 the test is done between the PBX and the 3CX servers so there should be no problem at all with stun phones trying to communicate. if you are getting failures it means that the PBX probably has no access to those ports due to the firewall.
 
I now have 5060 running but 10000 range is still having an issue with full cone NAT :(
 
If you don't resolve it, the PBX will work fine until it reaches that range (at which point you may lose audio until you restart the server).

Not sure if the beta firmware on the MX64 is the issue or if there is any error in the rules..
 
Not sure if the beta firmware on the MX64 is the issue or if there is any error in the rules..
I have rolled back the Beta already to see if that was the issue
 
Last edited:
  • Like
Reactions: hogan71088
Status
Not open for further replies.

Forum statistics

Threads
112,364
Messages
592,129
Members
165,538
Latest member
3K8iMGWviZ