- Joined
- Jul 5, 2024
- Messages
- 70
- Reaction score
- 27
Hello,
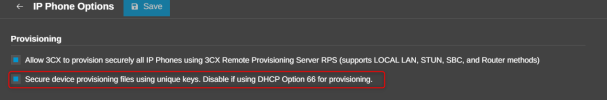
This might be a silly question, but I have a 3CX instance in the cloud (on Azure) and have added a Grandstream gateway. The gateway uses a provisioning link that points to an XML file. If I paste this link into my browser, I can see the credentials in plain text. Isn't this a bit problematic?
What if, for some reason, a bot or some other entity happens to come across this URL?
Could someone actually do anything with the credentials found in that file?
Thanks for your insights, sorry if this is a silly question and have a great weekend.
This might be a silly question, but I have a 3CX instance in the cloud (on Azure) and have added a Grandstream gateway. The gateway uses a provisioning link that points to an XML file. If I paste this link into my browser, I can see the credentials in plain text. Isn't this a bit problematic?
What if, for some reason, a bot or some other entity happens to come across this URL?
Could someone actually do anything with the credentials found in that file?
Thanks for your insights, sorry if this is a silly question and have a great weekend.